SSL inspection for schools: when you need it, and when DNS filtering will do
Almost every website now uses HTTPS. That protects students from snooping, but it also hides most of each request from the school filter.
SSL inspection (more correctly TLS inspection, also called HTTPS inspection) opens that traffic so the filter can see full page addresses. It is powerful, costly and sensitive, and many schools do not need it.
How SSL/TLS inspection works
An inspecting filter sits between the student and the website. It ends the encrypted connection, reads it, then opens a new encrypted connection to the real site.
Student device
Trusts the school's root certificate, installed in advance.
Inspecting filter
Decrypts, checks the full address and content against policy, then re-encrypts.
Website
Sees a normal encrypted connection from the filter.
Where it runs
On a firewall or web gateway on campus, in a cloud proxy that devices connect through, or in an agent on each device. Each choice changes cost and coverage.
What it reveals
Full page addresses, search queries, downloaded files and page content, for every connection it decrypts.
What it does not do
It does not decide what is harmful by itself. It still needs policy, category data and careful exemptions to be useful.
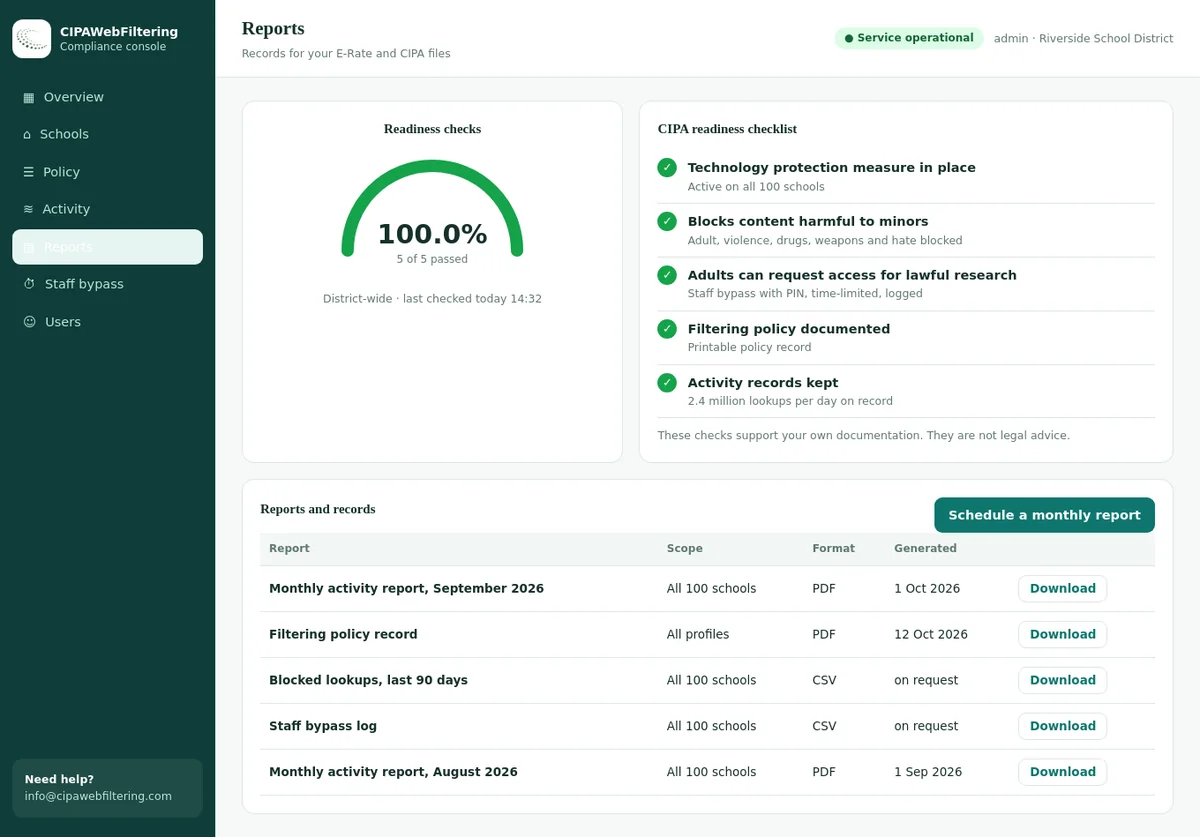
A CIPA filter that never touches the encrypted traffic
If your goals can be met by domain, you can skip certificates, decryption hardware and the privacy questions that come with them. Our hosted CIPA filter works at the DNS layer, so nothing is installed on computers.
- Decides by domain and does not look inside pages
- Adult and VPN/Proxy/Anonymizers are on in the CIPA preset
- Browser and public DNS settings that skip the filter are blocked by default
SSL inspection vs DNS-level filtering
Both can meet CIPA's technology requirement. They differ in what they can see, what they cost and what can go wrong.
SSL inspection
- Sees
- Full page address and content of HTTPS traffic it decrypts
- Can block
- Single pages, specific videos, search terms, file downloads
- Block page
- Shows a proper school block page on HTTPS sites
- Needs on devices
- A trusted root certificate on every device
- Runs on
- A firewall, proxy, gateway or device agent sized for decryption
- Main risks
- Broken apps, privacy exposure, hardware cost, support load
DNS filtering
- Sees
- The domain name each device looks up
- Can block
- Whole domains and subdomains by category or list
- Block page
- On HTTPS sites, usually a browser error rather than a branded page
- Needs on devices
- Nothing, or a DNS setting for devices that leave the network
- Runs on
- A hosted or local resolver; light on hardware
- Main risks
- Bypass through encrypted DNS, VPNs and proxies if not blocked
For a deeper comparison of the two approaches, read web filtering vs DNS filtering and CIPA DNS filtering for education.
When schools need SSL inspection, and when they do not
Start from what you need to block, not from the technology. If every goal can be met by domain, DNS filtering is simpler and safer.
Blocking parts of a site
Allowing a video platform but blocking specific channels or videos, or allowing a cloud drive but blocking certain shared folders.
Search term rules
Blocking or logging specific search terms requires seeing the query, which is inside the encrypted request.
Branded block pages
Showing a school page with a help message on HTTPS sites, instead of a browser error.
Blocking whole categories
Adult, gambling, proxy, weapons and similar categories are decided by domain. No decryption needed.
Meeting CIPA
CIPA asks for a technology protection measure, not a particular method. Domain-level category filtering is widely used to meet it.
Forcing SafeSearch
SafeSearch and YouTube Restricted Mode can be forced by DNS. See SafeSearch enforcement for schools.
Installing the inspection certificate on Chromebooks, Windows and iPads
Every device that is inspected must trust your filter's root certificate. Plan this per platform, and do it before you switch inspection on.
- Export the root certificate from your inspecting filter.
- In the Google Admin console, open the certificate settings under your device network settings.
- Upload the certificate and tick the option to use it as an HTTPS certificate authority.
- Apply it to the organizational units for students and staff devices.
- Wait for devices to sync, then turn inspection on for those units.
- Deploy the certificate to the Trusted Root Certification Authorities store.
- Use Group Policy for domain-joined devices, or your device management tool for cloud-managed ones.
- Check each browser: some keep their own certificate store and need a policy to trust system roots.
- Test desktop apps such as testing software, update services and conferencing tools.
- Add the root certificate to a configuration profile in your mobile device management tool.
- Push it to supervised devices before enabling inspection.
- For manually installed profiles on iPad, full trust must be turned on under Certificate Trust Settings.
- Test Safari and the classroom apps you rely on.
- Asking visitors and families to install a root certificate is a poor idea and often refused.
- Most schools do not inspect BYOD or guest networks; they use DNS category filtering there.
- Keep inspected and non-inspected networks clearly separated.
- See BYOD filtering in schools and guest wifi filtering.
Privacy and exemptions: what not to decrypt
Inspection gives the filter a view of sensitive traffic. A short, written exemption list protects students and staff, and reduces breakage.
| Exempt this | Category in our set | Why |
|---|---|---|
| Banking and payment sites | Online Banking, Financial Services | Staff and older students handle personal finances; decrypting this traffic adds risk and no safety value. |
| Health and medical services | Health & Medicine | Health information is sensitive, and students looking for help should not be exposed. |
| Government services | Government & Legal | Tax, benefit and identity portals hold personal data and rarely need inspection. |
| Crisis and support services | Your always-allow list | Students reaching help lines need privacy as well as access. |
| Pinned apps and update services | Your exemption list | Conferencing, testing and operating system updates often break under inspection. |
Log less
Keep full page addresses only as long as needed. Domain-level logs answer most questions.
Protect the key
The inspection private key can decrypt everything. Restrict access and rotate it if staff with access leave.
Tell people
State in your acceptable use policy that encrypted traffic may be inspected, and which categories are exempt.
Check your duties under FERPA and state student privacy laws. Our guide to student data privacy and filtering is a good starting point.
How the banking and health sites you would exempt are labelled
The exemption list on this page maps to categories, and these real entries show the labels you would use. A filter that works by domain never needs to decrypt them in the first place.
| Domain | Category |
|---|---|
| chase.com | Financial Services, Online Banking |
| paypal.com | Financial Services, Online Banking |
| wellsfargo.com | Financial Services, Online Banking |
| nami.org | Health & Medicine |
| 988lifeline.org | Health & Medicine |
The real costs and trade-offs of SSL inspection
The licence is rarely the biggest cost. Plan for these before you commit, and include them in any budget request.
Hardware capacity
Decryption takes far more processing than plain filtering. Appliances often reach much lower throughput with inspection on, so size for it.
Rollout time
Certificates on every managed device, testing per platform, and a pilot group before district-wide use.
Support tickets
Expect a wave of "this app stopped working" reports in the first weeks. Each one usually ends in an exemption.
Ongoing upkeep
New apps, certificate renewals, browser changes and exemption reviews every term.
Testing days
State testing platforms can be sensitive to inspection. Check each one's network guidance before test windows.
Privacy governance
Written policy, key protection, log limits and answers ready for parents who ask.
Protocol changes
Newer protocols such as QUIC are often blocked to force inspectable traffic, which can slow some services.
Encrypted Client Hello
Browsers have begun to support hiding the site name in the handshake. Watch browser policies, as this reduces what non-decrypting filters can see.
For a wider view of filter budgets, see how much a school web filter costs.
School web filter not blocking HTTPS? Common causes
This is one of the most frequent questions from school IT teams. The cause is usually one of the following.
| Symptom | Likely cause | Fix |
|---|---|---|
| A whole site blocks, but a single page you listed does not | The filter sees only the domain on HTTPS | Block at domain level, or inspect that site only |
| Blocked sites show a browser error, not your block page | Normal for DNS filters on HTTPS | Accept it, or inspect to show branded pages |
| Some students reach blocked sites | Encrypted DNS, VPN or proxy bypass | Block bypass routes. See blocking proxy sites |
| Every HTTPS site shows a certificate warning | Root certificate missing or not trusted on the device | Redeploy the certificate and check trust settings |
| One app stopped working after inspection began | Certificate pinning | Add the app's domains to the exemption list |
| Blocking works on campus, not at home | Devices off the school network | Device-level filtering. See off-campus enforcement |
A safe SSL inspection rollout plan
If you do decide to inspect, a careful sequence avoids most of the pain. Plan for a full term from pilot to district-wide use.
Write the purpose
List the specific goals inspection must meet. If DNS filtering already meets them, stop here.
Build the exemption list
Start with banking, health, government and known pinned apps before anything is decrypted.
Deploy certificates
Push the root certificate to every managed platform and confirm trust on sample devices.
Pilot with staff
Inspect one staff group or one lab first. Collect broken apps and fix them.
Expand by school
Roll out one building at a time, avoiding testing windows and the first week of term.
Review each term
Check exemptions, log retention, key access and whether inspection is still needed for each goal.
Letting an adult research page through without decrypting
Where inspection would be used to open one blocked page, our filter offers a staff PIN for 15, 30 or 60 minutes. It then switches back and logs the use, and VPN/Proxy stays blocked throughout.
Selective inspection: decrypt only where it adds value
Inspection does not have to be all or nothing. Many districts that inspect at all limit it to a few categories and groups, and filter everything else by domain.
Inspect
- Video platforms
- Where you want channel or video-level rules beyond Restricted Mode
- Search engines
- Where your policy calls for search term rules on top of forced SafeSearch
- Uncategorized sites
- New or unknown domains where a closer look at content is useful
- Student groups only
- Leave staff traffic out unless there is a clear reason
Pass through
- Sensitive categories
- Online Banking, Financial Services, Health & Medicine, Government & Legal
- Blocked categories
- Adult or proxy sites are blocked by domain anyway, so decrypting them adds nothing
- Trusted school tools
- Learning platforms, student information systems and testing services
- Pinned apps
- Anything that breaks under inspection
A selective approach cuts hardware load, support tickets and privacy exposure at once. It also makes your acceptable use policy easier to explain: you can tell families exactly what is and is not inspected, and why each choice was made.
Questions to ask before buying an inspecting filter
Use these in an RFP or a sales call. They work for any supplier and quickly show whether inspection fits your district.
Throughput
What throughput does the product reach with inspection on, at your peak student load?
Exemptions
Can exemptions be set by category, and how quickly are new banking and health domains covered?
Off campus
How does inspection work on devices at home, and what does that do to battery and speed?
Certificates
What help is there for certificate rollout on each of your device platforms?
Logs
What is logged by default, where, for how long, and who can see full addresses?
Breakage
Is there a maintained list of apps that fail under inspection?
Fallback
If inspection fails, does traffic fail open or closed, and can you choose?
Exit
How are certificates removed from devices if you change products?
Our school web filter RFP checklist covers the rest of the buying process.
Domain filtering through DNS compared with decrypting traffic
This is where our hosted filter sits, stated plainly.
| Consideration | Decrypting filter | Hosted CIPA filter |
|---|---|---|
| Device setup | Trust a certificate on every device | Nothing installed on computers |
| Hardware needs | Capacity for decryption | None, we run the DNS filter for you |
| Blocking a single page | Possible | Not possible; it decides by domain, not by page |
| Privacy exposure | Sees sensitive traffic unless exempted | Works from the domain name only |
| Meeting CIPA | Yes, with the cost above | CIPA preset, activity reports and a policy record |
| Laptops at home | Certificate and agent needed | Private encrypted link with the same rules |
SSL inspection in schools: FAQ
Does CIPA require SSL inspection?
No. CIPA requires a technology protection measure against prohibited visual depictions and an internet safety policy. It does not set a method, and many schools meet it with DNS or category filtering that does not decrypt traffic. See our CIPA compliance checklist.
Why is my school web filter not blocking HTTPS pages?
Without inspection, a filter sees only the domain of an HTTPS connection, so it can block a whole site but not one page. Bypass through encrypted DNS, VPNs or proxies and cached answers are other common causes.
How do I install an SSL inspection certificate on Chromebooks?
Upload the filter's root certificate in the Google Admin console certificate settings, tick the option to use it as an HTTPS certificate authority, apply it to the right units and wait for sync before turning inspection on.
Which sites should be exempt from SSL inspection?
Online banking and financial services, health and medical sites, government services and apps that break under inspection. Using categories for exemptions keeps the list current.
Does your hosted filter do SSL inspection?
No. Our hosted CIPA filter is a DNS filter that decides by domain category, so no certificates are needed. Our category data can also feed inspecting filters and firewalls schools already run.
Is SSL inspection a privacy risk?
It can be. Limit logging, exempt sensitive categories, protect the private key, tell users in your policy and check FERPA and state privacy duties.
Price is set by how many schools and devices you run, with a quote back inside one business day. If you are unsure whether DNS-level filtering is enough, a pilot at one site shows the blocks and reports first.
Related school filtering pages
Talk to us about your district
Not sure whether you need inspection at all? We can review your goals with you, show what DNS category filtering covers, and explain how our category data fits an inspecting filter you already run.
Talk to us about your districtGoogle, Chromebook and Chrome are trademarks of Google LLC. Windows is a trademark of Microsoft Corporation. iPad, Mac and Safari are trademarks of Apple Inc. Firefox is a trademark of the Mozilla Foundation. They are named here only to identify the products discussed. CIPA Web Filtering is not affiliated with, sponsored or endorsed by these companies.