CIPA Audits: What USAC Asks For
Every year your district certifies CIPA compliance on Form 486 or Form 479. Years later, USAC may ask you to prove it. This guide explains which reviews can touch CIPA, the documents reviewers ask for, the findings that come up most, and how to keep an audit-ready folder.
Where CIPA questions can come up in the E-Rate cycle
CIPA is certified once a year, but questions about it can arrive at several points, sometimes long after the funding year ends.
PIA review
Reviews your Form 471. CIPA is rarely the focus, but reviewers may ask for proof you follow program rules.
Form 486 review
USAC states it may review CIPA compliance before or after the Form 486 is processed.
Payment review
Payment quality reviews test whether disbursed funds were proper, and can ask for CIPA records.
Beneficiary audit
A full audit of selected funding years. CIPA compliance is one of the areas most often questioned.
Recovery and appeal
Findings can lead to funds being recovered. Decisions can generally be appealed, on strict deadlines.
The review types, and how much CIPA matters in each
Names and processes evolve, so match the letter you receive to the closest description here and read its instructions carefully.
Program Integrity Assurance (PIA)
CIPA: occasionalPIA reviews Form 471 applications before funding is committed: eligibility, discount rates, competitive bidding and similar.
Questions and answers run through EPC, and responses are usually due within 15 days. Ask for an extension early if you need one.
CIPA documents are not the usual focus here, but keep your folder ready in case a reviewer asks.
Form 486 review
CIPA: directForm 486 is where you certify CIPA status. USAC says it may review compliance before or after processing the form.
Questions here usually concern the CIPA option chosen, start dates, or a consortium's Forms 479.
See our E-Rate Form 486 CIPA certification guide for the options and deadline.
Payment Quality Assurance (PQA)
CIPA: frequentA review of a sample of payments to test whether disbursements were proper. It works like a condensed desk review, without site visits.
Requests typically cover documentation supporting the funds paid, which for internet access includes CIPA compliance.
Expect requests for the policy, hearing evidence and proof the filter was working.
Beneficiary audits
CIPA: frequentAudits of selected beneficiaries and funding years, carried out by USAC's audit staff or firms working on its behalf. These can include interviews and site visits.
USAC materials describe CIPA as one of the issues most commonly questioned in these audits.
The full document list below applies, often for more than one funding year.
What the CIPA preset blocks
The preset turns Adult and VPN/Proxy/Anonymizers on, which is the core of what a reviewer expects to see.
| Example site | Category that blocks it |
|---|---|
| playboy.com | Lingerie/Swimsuits/Intimate Apparel |
| nordvpn.com | File Sharing/P2P, VPN / Proxy / Anonymizers |
| torproject.org | VPN / Proxy / Anonymizers |
| protonvpn.com | VPN / Proxy / Anonymizers |
| bet365.com | Gambling, Sports & Recreation |
| usac.org | Government & Legal, Financial Services, Education/Reference |
What reviewers ask for, and what answers it
USAC's own guidance lists the CIPA records to keep. This table pairs each item with what usually satisfies it and the gaps we see most.
| What is requested | What usually satisfies it | Common gap |
|---|---|---|
| Internet safety policy | The policy in force during the audited funding year, covering minors' access to inappropriate material, safety in email and chat, unauthorized access, disclosure of personal information, and restricting harmful material. For schools, also online safety education. | Policy predates July 2012 and lacks the education element, or one of the five topics is missing. |
| Public notice and hearing | An agenda, published notice or minutes showing reasonable notice and at least one public hearing or meeting on the policy. At minimum, a record of when they occurred. | Hearing happened years ago; nobody kept the notice or minutes. |
| Policy adoption | Board minutes or a resolution showing the policy was adopted, with dates of later amendments. | Policy updated by staff but never formally adopted. |
| Description of the filter | A short document naming the filter, where it runs, which networks and devices it covers, and how the CIPA content types are blocked for minors and adults. | No written description; staff who set it up have left. |
| Proof the filter was working | Invoices or subscription records for the year, plus reports or logs from during the year showing filtering in operation. | Only a current screenshot; nothing from the audited year. |
| Forms 479 and 486 | Copies of the certified forms and Form 486 Notification Letters for the year, plus members' Forms 479 for consortia. | Consortium leader cannot find a member's 479. |
| Monitoring and education (schools) | The policy language on monitoring minors and online safety education, and evidence lessons happen, such as curriculum outlines or schedules. | Lessons happen but are not documented anywhere. |
Reports for the folder
Reports, the policy record and the log export are all part of the console. Keep a dated copy in each evidence folder.
An audit-ready CIPA folder
The simplest defense is a folder per funding year that anyone in the office can find. Here is a structure that works for districts of any size.
01 Policy /
internet-safety-policy-in-force.pdf
board-adoption-minutes.pdf
public-hearing-notice-and-minutes.pdf
02 Filter /
filter-description.pdf
subscription-invoices.pdf
monthly-reports / Jul ... Jun
network-and-device-coverage.pdf
03 Education /
online-safety-lessons-outline.pdf
04 Forms /
form-486-certified.pdf
form-486-notification-letter.pdf
form-479s (consortia)
05 Exceptions /
adult-research-access-log.pdf
Save reports monthly
Twelve small monthly filter reports prove operation across the year far better than a reconstruction made during an audit.
Write the filter description once
One page, updated when anything changes: product, where it runs, coverage, categories blocked by group, adult unblocking process.
Copy, do not link
Save PDFs of board minutes and notices into the folder. Links to old websites break, and audits can come many years later.
Name an owner
Usually the E-Rate coordinator. They check the folder is complete before each Form 479 or Form 486 is certified.
Prefer summaries to raw logs
Category summary reports show the filter worked without keeping every student's browsing for a decade.
Common CIPA findings, and how to prevent them
USAC training and audit materials describe the same few problems again and again. Each has a simple preventive fix.
Policy missing required elements
The policy does not address all the required topics, or a school policy lacks the online safety education piece.
No evidence of a hearing
The public hearing or meeting happened, or may have, but there is no notice, agenda or minutes to show it.
Certified, but filter not in use
An applicant certified compliance on Form 486 while the filter was not actually being used, or had lapsed.
Consortium member gaps
One member's policy or hearing evidence is missing, and the leader certified based on its Form 479.
Coverage gaps
A network, building or device type minors use was not routed through the filter for part of the year.
Records not kept
Documents existed once but were not retained for the full period after staff changes.
Keep the filter proof where you can reach it
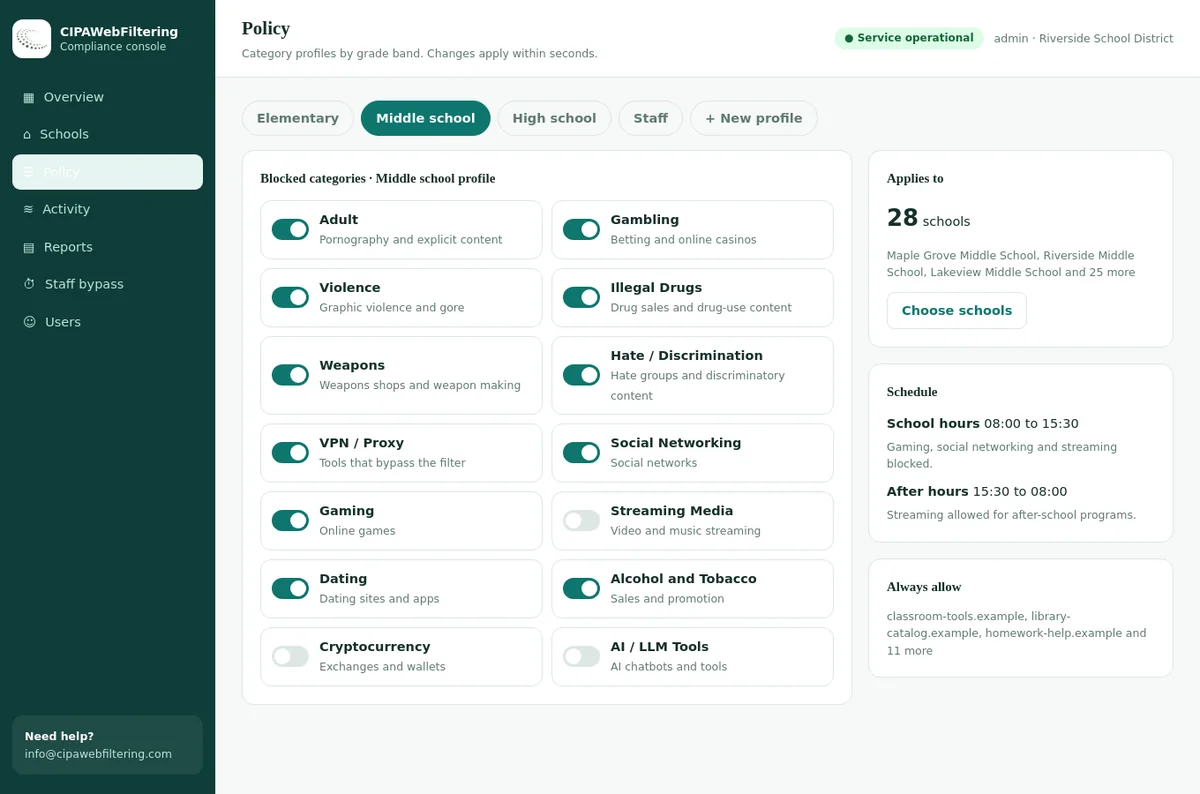
A CIPA reviewer wants to see that a technology protection measure exists and is working. The hosted filter produces that record as part of normal use.
- Activity reports show lookups and blocks for each school.
- The policy record shows which categories are on and when they changed.
- A log export hands the reviewer a file instead of a screenshot.
Responding to a CIPA document request
A request letter is not an accusation. Calm, complete and on-time answers resolve most reviews.
Note the deadline
Record the response date the same day. If you need more time, ask early and in writing.
Read the scope
Identify the funding years, entities and funding requests in question. Answer what is asked, for those years.
Call your adviser
Bring in your E-Rate consultant or counsel before sending anything substantive.
Pull the folder
Gather the policy, hearing, adoption, filter description, reports and forms for each year requested.
Explain gaps honestly
If something is missing, say so, explain what you have instead, and ask what alternative evidence is acceptable.
Keep a copy of everything
Save exactly what you sent, when and to whom, in the funding year folder.
If a finding goes against you
Most CIPA reviews close without a finding. When one does not, the process has clear steps, and acting quickly matters.
Recovery of funds
Possible outcomeUSAC cannot pay discounts for periods of non-compliance. A finding can lead to a commitment adjustment or recovery of funds already paid for the affected period.
The amount depends on the period and services affected.
Appeals
Strict deadlinesUSAC decisions can generally be appealed to USAC and then to the FCC. Deadlines are commonly 60 days from the decision date. Check the current rules on the day you receive a decision.
Work with your adviser; appeals succeed on evidence, not argument.
Run your own mock CIPA review
Once a year, pick a funding year from three to five years ago and try to answer a full request from the folder alone, in one afternoon. If you can, you are ready.
| Mock review question | Pass if you can show |
|---|---|
| Which internet safety policy was in force that year? | A dated PDF of that version, not the current one |
| When was it adopted, and by whom? | Board minutes or resolution with the date |
| When was the public hearing or meeting? | A notice, agenda or minutes naming the date |
| What filter was used, and where? | A filter description covering networks and device types |
| Was the filter working all year? | Invoices plus reports spread across the year |
| Were minors on every network covered? | A coverage note including guest and BYOD networks |
| How could adults request research access? | The documented process and any access log |
| How were students taught online safety? | A lesson outline or schedule for that year |
| What did we certify, and when? | Form 486 or 479 copies and notification letters |
Who should be involved in a CIPA review
CIPA evidence sits in three or four offices. A review goes smoothly when each one knows its part before a letter arrives.
E-Rate coordinator
Owns the folder, the deadline and the response. Coordinates everyone else and keeps copies of what was sent.
Technology department
Supplies the filter description, coverage map, reports and invoices, and explains configuration if asked.
Board clerk or secretary
Finds adoption minutes, hearing notices and agendas, often from years before current staff arrived.
Curriculum office
Provides evidence of online safety education, such as lesson plans or digital citizenship schedules.
E-Rate adviser
Reads the request, advises on scope and alternatives, and reviews the response before it goes out.
Consortium leader
For consortium funding, provides members' Forms 479 and coordinates member evidence.
Making filter evidence effortless
The filter half of a CIPA review is the part IT controls directly. A few settings turn evidence into a by-product of normal operation.
Scheduled reports
Set the filter to email a monthly category summary for each school and network to a shared mailbox that feeds the CIPA folder.
Category-based blocking
Blocking whole categories, rather than hand lists, shows a consistent method. Our database covers 120 million domains in 58 categories.
Periodic tests
Run a dated school web filter test each term and save the results with the year's records.
Binder or console
Where audit evidence comes from
| Item reviewers ask for | Assembled by hand | From our hosted filter |
|---|---|---|
| Filter is in place | Screenshots | Policy record from the console |
| Adult and VPN blocking | Manual test notes | CIPA preset with both categories on |
| Staff overrides | Paper form | Logged PIN bypass |
| Per-school settings | Spreadsheet | Separate settings in one console |
| Activity history | Gaps possible | Reports and log export |
CIPA audit FAQ
What documents does USAC ask for to prove CIPA compliance?
USAC guidance lists the internet safety policy, evidence of public notice and a public hearing or meeting, evidence the policy was adopted, a description of the technology protection measure, documentation showing the filter was installed and working during the funding year, and copies of Forms 479 and 486 as applicable.
How long do we have to keep CIPA records?
Current USAC guidance says at least 10 years after the later of the last day of the funding year or the service delivery deadline for the funding request. Some older materials quote shorter periods, so follow current guidance.
Does PIA review CIPA compliance?
Program Integrity Assurance reviews focus on the Form 471 application, such as eligibility, discounts and competitive bidding. Reviewers can ask for proof that you are following program rules, and responses are usually due within 15 days in EPC. Detailed CIPA document requests are more typical of payment reviews and audits after funding.
What are the most common CIPA audit findings?
USAC materials describe findings such as internet safety policies missing required elements, no evidence of a public hearing or notice, and applicants that certified CIPA compliance while the filter was not actually in use.
What happens if we cannot find proof of our public hearing?
USAC guidance says some minor, immaterial errors can be corrected before funds are recovered, and gives holding a public hearing as an example when a record of an earlier hearing cannot be found. Talk to your E-Rate adviser before responding.
Can we appeal a CIPA audit finding?
USAC decisions, such as a funding recovery, can generally be appealed to USAC and then to the FCC. Appeal deadlines are strict, commonly 60 days from the decision, so check the current rules as soon as you receive a decision.
Do filter logs have to be kept for the whole funding year?
USAC asks for reports or other documentation showing the filter was installed and working during the funding year. Full logs are not required by name. Periodic summary reports, saved monthly, are usually a practical way to show operation across the year with less personal data.
Related CIPA guides
General information for school and library staff, not legal advice. USAC review programs, names and deadlines change; confirm details with current USAC guidance and your E-Rate adviser.
What you pay depends on the schools and devices involved, and our quote comes within one business day. You can begin with a single site, and look at the blocks and reports before signing.
Be ready before the letter arrives
We help districts run category filtering that produces CIPA evidence automatically, month by month, for every school and network.
Talk to us about your district